

 admin
Federal agents just pulled the plug on a sneaky network of “laptop farms” that allegedly funneled U.S. corporate work and money back to North Korea. The operation shows how foreign adversaries can skirt sanctions, steal identities, and hide inside plain sight of American companies. If you still think remote hiring is harmless, this should be a wake-up call.
What the FBI found
Operation Lonestar Roundup
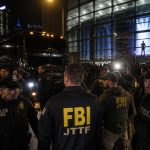
The Justice Department and the FBI, with help from cybersecurity firm CrowdStrike, executed a coordinated sweep across Texas and elsewhere. Agents searched more than 40 homes and seized roughly 187 laptops and KVM devices tied to what they call a “major illicit laptop‑hosting network.” Prosecutors say the probe led to charges against multiple people and arrests in Ohio tied to schemes that affected dozens of U.S. employers.
How the laptop farms operated
Here’s the ugly mechanics: operatives used stolen or fake American IDs and VPNs to look like U.S. remote workers. Employer laptops were routed to U.S.-based facilitators who configured the devices and installed remote‑access tools so workers in North Korea could log in. The group tracked by CrowdStrike, labeled FAMOUS CHOLLIMA, allegedly turned legitimate remote jobs into a revenue stream for the DPRK and a backdoor into corporate systems.
National security and corporate risk
Law enforcement is clear: this is not just fraud or payroll theft. The Justice Department says the money and access can feed North Korea’s weapons and intelligence programs. Companies lose money, data and trust. Worse, a compromised laptop can give hostile actors persistent access to sensitive networks. Arrests and seizures help, but experts warn these groups adapt fast — so complacency is not an option.
Practical steps and a blunt political take
Companies must tighten vetting for remote hires, lock down device management, and treat unusual pay flows as a red flag. And yes, give the FBI and CrowdStrike credit for doing the heavy lifting — but don’t pretend this is a one-and-done victory. If American businesses want to sleep better, they need stronger identity checks, better device controls, and a little common sense about who they let connect to their networks. Otherwise, expect more laptop farms to pop back up like weeds.